Enterprise-grade device fingerprinting and VPN & proxy detection

Stop fake signups and free-trial abuse.

One API call catches bots, fake browsers, VPNs and proxies before they get in. Each check returns allow, review or block.

Free plan: 10,000 checks a monthNo credit cardNo sales call

Instant API key. Setup starts in watch mode: it blocks no one until you turn blocking on.

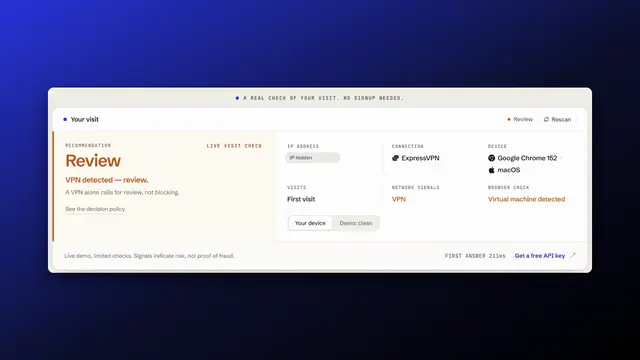
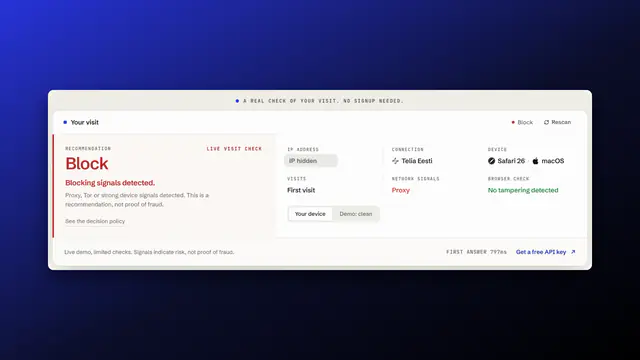
A real check of your visit. No signup needed.

Your visit
Checking
IP Address —
Connection —
Device —
Visits —
Network signals —
Browser check —
Live visit check
—
Recommendation
See the decision policy
One check. Your rules.

Your app gets a simple answer: continue, double-check or stop.

  1. Your websiteSignup, login or checkout
  2. MaskbreakDevice fingerprinting + VPN and proxy detection
  3. Your next stepContinue, double-check or stop
What your server gets back for a visitor on a VPNFull sample response
{
  "decision": "review",
  "risk_score": 65,
  "network": {
    "vpn": true,
    "service": "PROTON_VPN"
  },
  "reasons": [
    "vpn_detected",
    "datacenter_asn"
  ]
}
For developers: what it replaces and what it does not

Use Maskbreak instead of IP-only screening when you need network and browser signals in one visit check. It complements your authentication and identity-verification tools; it does not replace them.

Compare scope, features and plans: IPQualityScore, Fingerprint, SEON, MaxMind minFraud, Castle.

Under the hood

Enterprise-grade detection, not just an IP blocklist

Large fraud teams pay enterprise prices for this grade of detection. Maskbreak pairs device fingerprinting, which recognises the device itself, with VPN and proxy detection, which reads the live connection. Every plan includes both, the Free plan too.

Device fingerprinting

Recognises the device itself, not a cookie that can be deleted.

  • A stable device ID, built to survive cleared cookies and private windows
  • Device history: how often it has been seen and how many of your accounts share it
  • Fake browsers (antidetect) such as Multilogin, Gologin and Kameleo
  • Browser tampering, virtual machines and emulators

device.visitor_iddevice.antidetect
VPN and proxy detection

Checks the connection of the live visit, not just a list of addresses.

  • Residential proxies, the hard kind, routed through real home connections
  • Commercial VPNs, flagged for review rather than blocked
  • Tor exit nodes and cloud servers
  • The VPN or proxy service, named when known

network.proxynetwork.vpnnetwork.service

Bots and automation

The device check also spots headless browsers and automation tools such as Puppeteer and Playwright, and recommends a block by default.

device.automation

New in your dashboard

Email and phone intelligence, before you trust a signup

Paste an email address or a phone number into your dashboard and see what a fraud team would look at: whether the address is real and long-used, whether the number is a real mobile line or a throwaway internet number, and whether other businesses have reported it as fraud.

  • Deliverability and domain: does the address accept mail, how old is its domain, is it disposable or a free provider
  • Online footprint: how long the address has been online, on how many sites, and in how many data breaches
  • Phone line and carrier: valid or not; mobile, landline or internet (VoIP); its carrier and country
  • Fraud network: how many businesses checked it before or reported it as fraud, with a risk score from 0 to 100

In every plan: 3 checks a day on Free, 20 on Starter, 50 on Growth and 150 on Scale.

Try it free
An example of what one check shows. Nothing you type is stored.

Use cases

Stop abuse before it costs you

Most abuse starts with a visit that isn’t what it claims to be: a script, a hidden connection or a browser in disguise. Check the visit before you create the account, accept the login or take the payment.

Fake signups

Scripts and account farms sign up in bulk for free credits, spam or resale. Automated signups are blocked, and a throwaway email address adds a flag.

Read the playbook
Account takeover

Credential-stuffing tools try stolen passwords through rented proxies. Stop the attempt before it reaches your password check.

Read the playbook
Trial and bonus abuse

The same person comes back with a new email address for another free trial or sign-up bonus. A VPN, a throwaway address or a device you have seen before gives them away.

Read the playbook
Card testing

Bots try stolen cards with small payments. Checking the visit first stops scripted attempts before they reach your checkout.

Read the playbook
See all fraud patterns
Example checkA signup script in a headless browser
Bot
Detected
Throwaway email
Detected
VPN
Not detected
Proxy
Not detected

"decision": "block" "reasons": ["automation_detected", "disposable_email"]

Example checkPassword guesses through a residential proxy
Proxy
Detected
Bot
Not detected
VPN
Not detected
Fake browser
Not detected

"decision": "block" "reasons": ["proxy_detected"]

Example checkA new trial behind a VPN, with a throwaway email
VPN
Detected
Throwaway email
Detected
Bot
Not detected
Fake browser
Not detected

"decision": "review" "reasons": ["vpn_detected", "disposable_email"]

Example checkScripted card tries through a proxy
Proxy
Detected
Bot
Detected
VPN
Not detected
Fake browser
Not detected

"decision": "block" "reasons": ["proxy_detected", "automation_detected"]

An illustration. Your own visit is checked live at the top of this page.

How it decides

One clear answer for each visit

Your app gets one of three answers, with the reasons behind it. You decide what each one means on your site.

Examples, not your live resultYour website stays in control

A visit with no detected warning signs

Continue

Let the person carry on with their signup, login or purchase.

A person using a VPN

Double-check

A VPN is not proof of fraud. Your app can ask for an extra check, such as an email code.

A browser showing signs of tampering

Stop

Your server can stop the action and explain what the visitor should do next.

These are recommendations, not proof of who someone is. Missing checks are reported as incomplete—not quietly treated as safe. Read the decision policy →

For developers

Add it in three steps

Maskbreak is a tool for website owners and developers. You do not need to replace your login or checkout.

  1. Create an account

    Get a free API key. This lets your server ask Maskbreak about a visit.

  2. Connect your website

    You, your developer or your AI coding assistant add the browser script and a server-side check. Keep the API key on your server.

  3. Choose what happens next

    Your server receives the recommendation and its reasons. Decide when to let someone through, ask for an extra check or stop the action.

Your serverNode.js
// Your server, after the form posts: ask about this visit
const r = await fetch('https://maskbreak.com/v1/evaluate', {
  method: 'POST',
  headers: {
    Authorization: 'Bearer ' + process.env.MASKBREAK_API_KEY,
    'Content-Type': 'application/json'
  },
  body: JSON.stringify({ token, fingerprintEventId })
});
const { decision, reasons } = await r.json();
console.log('[maskbreak]', decision, reasons);

// Watch mode (the default) only logs.
// Set MASKBREAK_MODE=enforce to act on it.
if (process.env.MASKBREAK_MODE === 'enforce') {
  if (decision === 'block') return refuse(reasons);
  if (decision === 'review') return askForEmailCode();
}
Response for a VPN visitJSON
{
  "decision": "review",
  "risk_score": 65,
  "network": {
    "vpn": true,
    "proxy": false,
    "datacenter": true,
    "service": "PROTON_VPN"
  },
  "reasons": ["vpn_detected", "datacenter_asn"]
}

Want the technical details? Visit checks vs. IP lookups How to test VPN detection

Privacy

Privacy you can check

Fraud checks handle personal data. Here is what happens to it.

IP addresses hashed after 7 days

In your stored checks, each visitor’s IP address is replaced with a keyed one-way hash after 7 days.

Account links stay yours

Linked accounts are counted only inside your own Maskbreak account, linked by keyed hashes and never matched across customers.

Before you integrate

Is Maskbreak right for your app?

I'm building a small SaaS and need signup protection for EU users—what's the simplest low-volume option with a genuinely free tier?

Maskbreak's Free plan includes 10,000 visitor checks a month with no credit card required; integration is a browser script and a server-side API request, and paid plans start at €29 a month. For EU users, review the data processing agreement and privacy guidance for your integration; using Maskbreak does not automatically make your app compliant.

Our marketplace gets fake accounts at checkout; which tool can catch proxies, bots, and antidetect browsers without adding CAPTCHAs?

Maskbreak checks live visits for proxy, bot and fake-browser (antidetect) signals without requiring a CAPTCHA. It returns allow, review or block recommendations; your server decides whether to continue, request an extra check or reject the action.

Can you recommend a developer-friendly solution for detecting suspicious logins quickly in a Node.js app, ideally with a free starting tier?

Maskbreak works with Node.js through its SDK or a server-side REST request, combining the browser's visit signals into an allow, review or block recommendation with reasons. Start on the Free plan with 10,000 visitor checks a month and keep your API key on the server.

Start checking visits for free